
4 November 2026 / 6 minutes of reading
Phishing Without Typos or Bizarre Promises: Would You Spot It?
Modern phishing is no longer easy to identify by typos or bizarre promises. Try ten realistic workplace scenarios and see whether you can distinguish a scam from legitimate communication.
If a “long-lost” uncle from Nigeria emailed you today about a million-dollar inheritance in broken English, you would probably delete the message immediately. Would you do the same with a work email from a colleague? AI-powered phishing campaigns can now convincingly imitate everyday workplace communication. Test yourself with ten scenarios and find out whether you can spot the scams.
A scam can become part of your working day
Phishing is a social engineering technique in which an attacker tries to obtain sensitive information or persuade you to act in their interests. You might enter your password on a fake website, open a malicious attachment, or disclose your payment card details. Today’s traps no longer need to contain typos, awkward wording, or unrealistic promises.
A creative attacker will construct a situation that makes perfect sense. You may be expecting an invoice, working with a shared document, or trying to regain access to an account. The message arrives at the right moment, looks familiar, and offers a simple next step. The attacker needs you to take that step before checking who is asking you to do it.
Email is only one of the available channels. A skilled fraudster can send a text message that your phone places in the same conversation where a trusted institution recently sent you a legitimate message. The information we voluntarily share on social media also helps attackers recreate familiar contexts and convincingly impersonate colleagues or managers.
Why recognizing the warning signs is not enough
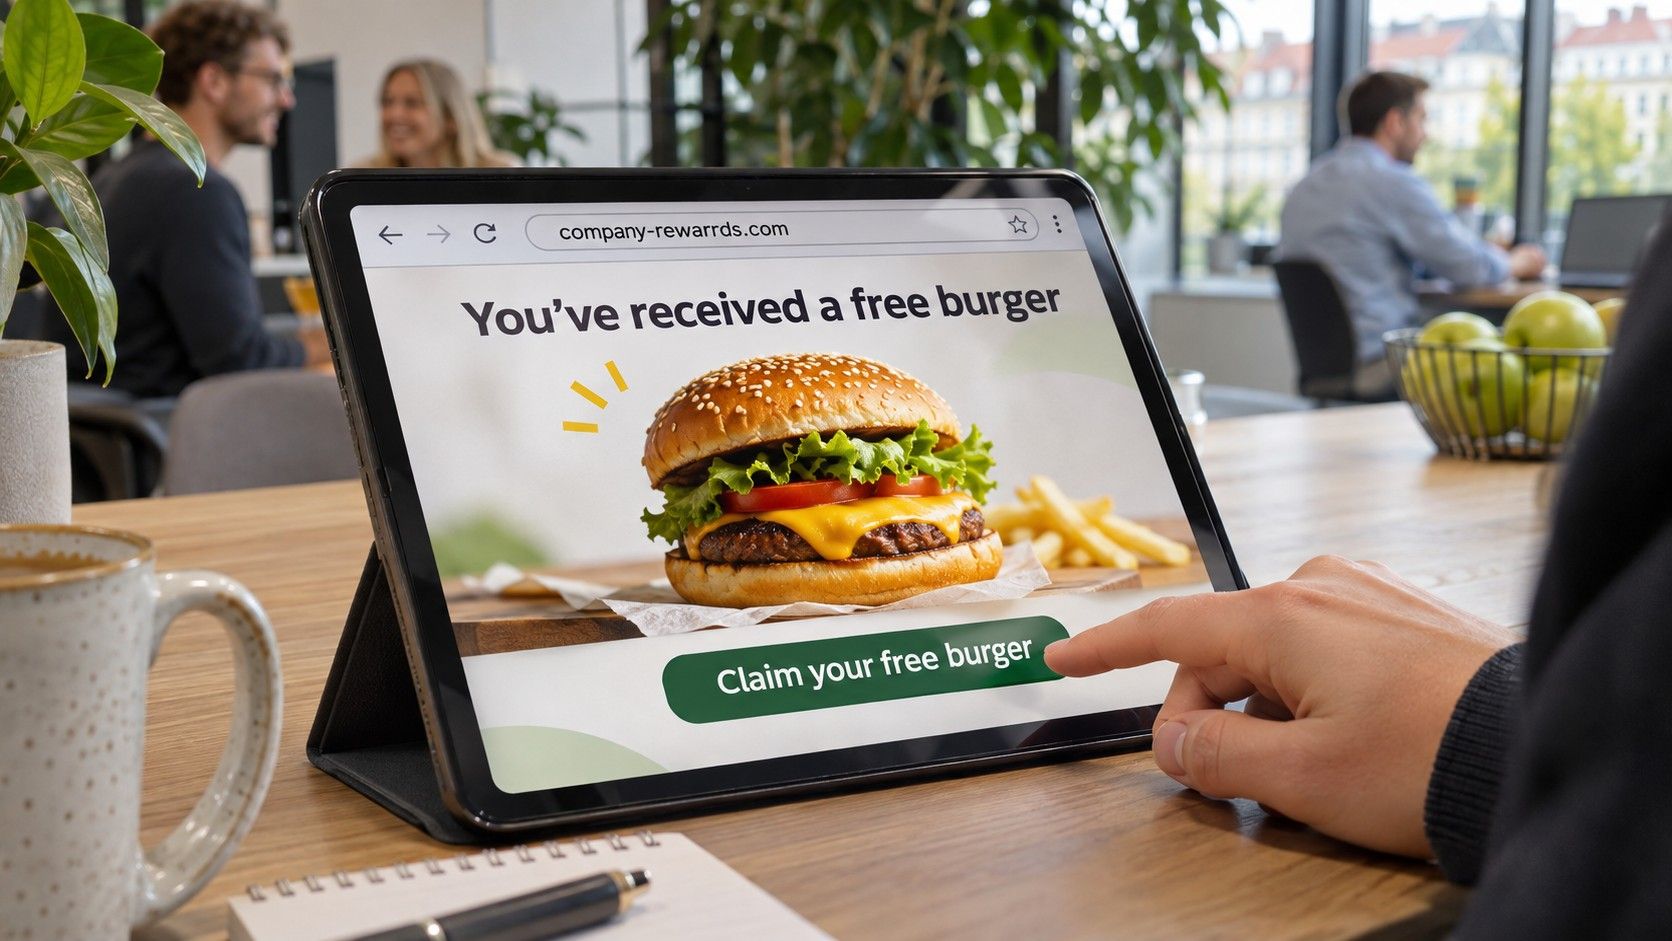
It is nine o’clock in the morning, and you have just received a message from your manager. They apparently need you to review a document quickly before a meeting. The link opens a login page that looks like a company service you use every day. During a busy working day, you may not hesitate and simply assume that signing in is part of the process.
The attack relies on familiar psychological triggers such as authority, urgency, and the desire to help. This is why even someone who has completed security training can hesitate despite knowing the basic security rules. Being able to explain phishing and recognizing it during a busy working day are two different things.
When faced with an unexpected request, take a moment to pause. Does the message match what you are currently working on? Where does the link really lead? If someone asks for sensitive information or an unusual action, verify the request through a known contact or another communication channel. A familiar sender name or logo alone does not make a message trustworthy.
What to expect from the phishing quiz
At Citadelo, we have created a short phishing quiz based on situations from everyday working life. You will encounter emails, phone messages, and login pages. Some are fraudulent, while others are entirely legitimate. Your task is to decide which ones you can trust.
Marking every example as fraudulent will not guarantee a good result. The quiz also counts false alarms as mistakes, so it tests not only caution but also your ability to distinguish an attack from legitimate communication. It takes approximately five minutes and requires no registration. If you provide your email address at the end, we will send you a certificate with your result and a practical guide to recognizing phishing campaigns.
The quiz can also be a simple way to start a discussion about employee preparedness within your organization. Training provides an essential foundation, but a realistic simulation shows how people and security processes respond in practice. The quiz does not replace a simulated phishing campaign, but it offers a straightforward first step.
Can you assess all ten scenarios correctly?
The quiz takes approximately five minutes and can be completed without registration.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2026 citadelo AG. All rights reserved.


