
Social engineering
Social engineering
The human factor has always been, and will continue to be, the most common attack vector in corporate cybersecurity. Social engineering is an ethical hacking technique that uses psychological tactics and the manipulation of human behaviour to obtain sensitive information or trigger unauthorised actions.
Through realistic simulated attacks, we assess whether your employees can recognise phishing, fraudulent phone calls, or other forms of manipulation before they give attackers access to corporate systems and sensitive data.
Book a free consultation

We are trusted by Fortune 500 companies worldwide


How does social engineering work?
You may have the most advanced firewalls, multi-factor authentication, and sophisticated threat detection in place. Yet one careless click, a disclosed password, or a convincing phone call from an attacker may be enough to compromise your organisation’s security.
Attackers impersonate colleagues, senior executives, suppliers, or technical support staff. They exploit trust, inattention, and time pressure to persuade employees to open a malicious attachment, enter their login credentials, or perform an unauthorised action.
With the rise of artificial intelligence, these attacks are becoming increasingly convincing, targeted, and difficult to detect. Phishing emails no longer need to contain grammatical errors. They can be personalised using information obtained from public sources and combined with fraudulent phone calls, impersonation, spoofing, voice cloning, or deepfake content.
Through carefully designed social engineering scenarios, we test your organisation’s resilience in practice. The goal is not to catch employees out, but to determine how they would respond to a real attack, whether they would report it correctly, and which security processes need to be improved.
The most common types of attacks
Nearly 40% of employees fell for a simulated attack
Our experience shows that during initial testing, a significant proportion of employees may fall for a simulated phishing or vishing attack. In some cases, ethical hackers managed to deceive as many as 40% of the people tested.
Attackers often need nothing more than a convincing email, a persuasive phone call, and information about the company or its employees obtained from publicly available sources. By combining phishing and vishing, they can make the scenario more credible and create pressure to act quickly.
A successful social engineering attack can lead to stolen login credentials, unauthorised access to corporate systems, fraudulent payments, or the disclosure of sensitive information. A single careless action by an employee can give attackers an entry point into an otherwise well-protected organisation.
Phishing testing reveals how many employees open a fraudulent message, click a link, provide requested information, or correctly report the attack. Social engineering testing provides real data about employee security awareness, vulnerable groups, and the effectiveness of internal processes.
A simulated attack allows you to identify weaknesses safely and in a controlled environment before a real attacker can exploit them.
Phishing
Phishing is the most widespread form of social engineering conducted by email. The attacker impersonates a trusted person or organisation, such as the IT department, company management, a bank, or a supplier, and attempts to persuade an employee to enter login credentials, open a fraudulent link, or download a malicious attachment.
Vishing
Vishing is a fraudulent phone call in which the attacker poses as a colleague, technical support specialist, supplier, or representative of a trusted institution. Using a convincing story and time pressure, the attacker attempts to persuade an employee to disclose sensitive information or perform a requested action. A spoofed phone number or an AI-generated voice can make the call appear even more credible.
Smishing
Smishing uses text messages or communication platforms such as WhatsApp, Messenger, or Telegram. The attacker may alert an employee to a password change, security incident, parcel delivery, or another urgent situation and use a fraudulent link or reply to obtain sensitive information.
What other social engineering attacks do we test?
Phishing, vishing, and smishing are among the best-known attacks targeting the human factor. In more targeted scenarios, however, attackers also use whaling, spear phishing, spoofing, or tailgating. These techniques can be combined to make an attack more convincing and gain access to sensitive information, corporate systems, or restricted premises.
01
Whaling
Whaling is a highly targeted phishing attack aimed at CEOs, senior executives, or other key decision-makers within an organisation. Attackers use information about their position, authority, responsibilities, and business relationships to create convincing requests for payments, sensitive data, or confidential business actions.
02
Spear phishing
Spear phishing is a targeted attack designed for a specific person or group of employees. Attackers use information about their role, colleagues, current projects, or business relationships to make the message appear highly credible. We also frequently use spear phishing as part of broader Red Teaming exercises.
03
Spoofing
Spoofing allows attackers to impersonate a trusted person, colleague, or organisation by falsifying an email address, phone number, or sender identity. When combined with phishing or vishing, it makes fraudulent messages and calls appear more credible and increases the likelihood that the target will respond.
04
Tailgating
Tailgating is a physical attack in which an unauthorised person enters restricted premises alongside an employee without using their own access credentials. The test examines whether staff verify access rights, follow internal security procedures, and respond appropriately when an unknown person moves around the organisation.
05
Clickjacking
Clickjacking is a technical vulnerability that tricks users into clicking a hidden or disguised website element instead of the content they intended to select. As it is not a conventional social engineering method, we primarily assess this type of attack as part of web application penetration testing.
How does a social engineering test work?
We tailor every social engineering test to your organisation’s environment, risks, and security objectives. The entire process is agreed in advance to ensure that it realistically tests employees and internal processes without disrupting normal operations.
Together, we define what the simulated attack should assess, which employee groups will be included, and which boundaries must not be crossed. We also establish rules to protect employees, sensitive data, and the organisation’s normal operations.
We create a credible scenario based on your industry, working environment, and selected target groups. For targeted attacks, we may also use publicly available information about the company and its employees.
We launch the agreed phishing, vishing, smishing, or other social engineering attack. The simulation is conducted in a controlled manner without genuinely malicious content, ensuring that corporate systems, sensitive data, and normal operations are not put at risk.
We monitor how employees respond to the simulated attack. We assess whether they opened a fraudulent message, clicked a link, provided requested information, or recognised and correctly reported suspicious activity to the security team.
We present the results in a clear report identifying the most significant risks, vulnerable groups, and weaknesses in internal processes. We propose specific measures, training, and further steps to improve the organisation’s resilience.
What will you receive after the test?
The result of social engineering testing is not simply the percentage of employees who fell for simulated phishing, vishing, or another attack. We show you why a particular scenario succeeded, which groups were most vulnerable, and whether employees knew how to report suspicious activity correctly. We turn these findings into specific recommendations that allow you to improve security awareness, internal processes, and your organisation’s overall preparedness for a real attack.
Through social engineering testing, we identify weaknesses in employee behaviour and internal security processes before a real attacker can exploit them.
Book a free consultation
Executive summary
Company management receives a concise overview of the most important results, identified risks, and recommended next steps. The summary explains the business impact of the findings without unnecessary technical detail.
Detailed test results
The report evaluates the individual stages of the simulated attack and the responses of the employees tested. It shows message open rates, clicks, information disclosures, and the number of correctly reported attempts.
Analysis of vulnerable groups
We identify the teams, job roles, or employee groups that were most vulnerable to the simulated attack. The results allow you to target subsequent training and security measures more effectively.
Recommendations for improvement
We propose specific measures to improve security awareness, modify internal processes, and strengthen the reporting of suspicious activity. We also recommend an appropriate scope for further training or repeated testing.
Based on the results, we can also prepare targeted cybersecurity training and use a follow-up test to verify whether employee resilience has improved.

What happens after the test?
We evaluate the test results, propose specific measures, and prepare targeted cybersecurity training. Follow-up testing then allows us to determine whether your employees have become more resilient to social engineering attacks.
Explore our security training
What are the benefits of social engineering testing?
A social engineering test provides real data on how employees respond to phishing, vishing, smishing, and other manipulation techniques. Instead of relying on general assumptions, you will learn which groups are most vulnerable, whether employees can report attacks correctly, and where security processes need improvement.
Real data on employee responses
You will discover how many employees opened a fraudulent email, clicked a link, provided requested information, or performed another risky action. Phishing testing also shows how many employees recognised and correctly reported the attack.
Identification of vulnerable groups
We identify the teams, job roles, and employee groups that were most vulnerable to the simulated attack. You can then target subsequent training and security measures at the people and processes where they will have the greatest impact.
Improved security awareness
Employees gain practical experience with phishing, vishing, or another form of social engineering. They learn to recognise warning signs more effectively and understand how their decisions can affect the security of the entire organisation.
Verification of internal processes
We assess whether employees know how and to whom they should report suspicious communication. Testing also reveals whether the security team can evaluate the report correctly and respond to a potential incident in time.
Who is social engineering testing for?
Social engineering testing is suitable for organisations that want to assess their employees’ resilience to phishing, vishing, smishing, and other attacks targeting the human factor. It is particularly important for companies that work with sensitive data, financial assets, or critical systems, where the failure of a single employee could result in a serious security incident. Simulated attacks help identify high-risk job roles, gaps in security awareness, and weaknesses in the process for reporting suspicious activity.
Book a free consultation
Do you want to assess employee security awareness?
Conventional training may not reveal how employees will behave under the pressure of a real attack. A simulated phishing test assesses their responses in practice and reveals whether they can recognise and correctly report a fraudulent message or phone call in time.
Do you work with sensitive data or financial assets?
Social engineering attacks often target employees with access to personal data, corporate accounts, or internal systems. Testing helps determine whether they can resist manipulation and follow security procedures even under time pressure.
Do you want to test high-risk teams and job roles?
We can target spear phishing and vishing at company management, IT administrators, finance departments, reception staff, or other employees with sensitive privileges. The results reveal which groups need more targeted training or better processes.
Do you need to verify the effectiveness of security training?
Completing a training course does not guarantee that employees can recognise a convincingly prepared attack. Repeated social engineering testing shows whether their behaviour is improving and whether the training programme is producing the expected results.
Are you preparing for an audit or regulatory requirements?
Test results provide real data on employee security awareness and the effectiveness of internal processes. They can support cyber risk management, security audits, and evidence of implemented organisational measures.
More about social engineering
Find out why phishing attacks continue to succeed, what mistakes companies make when protecting employees, and how weak login credentials increase the likelihood of a successful attack.
All articles about social engineering
How social engineering testing supports NIS2, DORA, and ISO 27001
Legislation and security standards emphasise the management of cyber risks associated with the human factor, security awareness, and employee training. However, adopting internal policies or completing training is not enough. Organisations should be able to assess whether employees can apply what they have learned during a realistic attack.
Social engineering testing helps verify the effectiveness of implemented measures in practice. Simulated phishing, vishing, or smishing demonstrates how employees respond to manipulation attempts, whether they follow established procedures, and whether they can report a suspicious situation in time. Test results can support human risk management and compliance with NIS2, DORA, and an information security management system based on ISO/IEC 27001.
Social Engineering and NIS2
NIS2 includes basic cyber hygiene practices and cybersecurity training among its cybersecurity risk-management measures. Simulated phishing, vishing, or smishing can assess whether employees can recognise an attack, report it correctly, and follow internal rules.
Social Engineering and DORA
DORA requires financial entities to implement security awareness programmes and digital operational resilience training. A social engineering test can provide measurable results that help identify risky behaviour, improve training, and subsequently evaluate its effectiveness.
Social Engineering and ISO/IEC 27001
ISO/IEC 27001 emphasises risk-based information security management. It also covers security awareness, education, and training. Simulated attacks can help assess the effectiveness of implemented measures and identify areas requiring further education or process improvements.
Frequently asked questions
Questions we most frequently receive about phishing testing and other forms of social engineering testing.
Yes. Based on the test results, we can prepare targeted cybersecurity training focused on the most common mistakes, risky situations, and specific types of attack. Follow-up testing can then verify whether employee security awareness and resilience have improved.
The outcome includes an overview of employee responses, identification of vulnerable groups, and an evaluation of internal processes. The report shows metrics such as fraudulent message open rates, clicks, information disclosures, and correctly reported attempts. It also contains specific recommendations for improving security awareness, training, and internal procedures.
Spear phishing is a targeted phishing attack designed for a specific person or group of employees. It uses information about their roles, colleagues, projects, or business relationships, making it more credible than mass phishing. Yes, we test spear phishing both independently and as part of comprehensive Red Teaming exercises.
To assess genuine responses, the employees being tested are generally not informed about the specific scenario in advance. Only designated individuals within the organisation are aware of the test. We always define the scope, rules, evaluation methods, and employee protections before testing begins.
Yes. Testing follows a pre-approved scenario and does not use genuinely malicious content. We define the boundaries of the test to ensure that corporate systems, sensitive data, employees, and normal operations are not put at risk.
We test phishing, spear phishing, whaling, vishing, smishing, spoofing, pretexting, and selected physical social engineering scenarios, such as tailgating. We can combine individual techniques according to the organisation’s environment, risks, and security objectives.
Social engineering is a broader term for attacks that exploit human manipulation. Phishing is one of its most common forms and is primarily conducted by email. Other forms include vishing, smishing, pretexting, and tailgating.
Yes. We can target specific teams, job roles, or employees with access to sensitive data and systems. Common targets include company management, IT administrators, finance departments, help desks, and reception staff.
The appropriate frequency depends on the organisation’s risk profile, the results of the initial test, and changes in the working environment. We recommend repeating tests regularly, as well as after training, significant process changes, or the onboarding of a large number of employees. Follow-up testing reveals whether the implemented measures are actually effective.
Yes. We prepare the scenario according to your industry, working environment, internal processes, and selected target groups. For targeted testing, we may also use publicly available information about the company and its employees to ensure that the simulation reflects real-world threats.
Social engineering testing focuses primarily on the human factor, employee responses, and the process for reporting suspicious activity. Red Teaming assesses the resilience of the organisation as a whole and may combine social engineering with digital attacks, physical intrusion, and security team response testing.
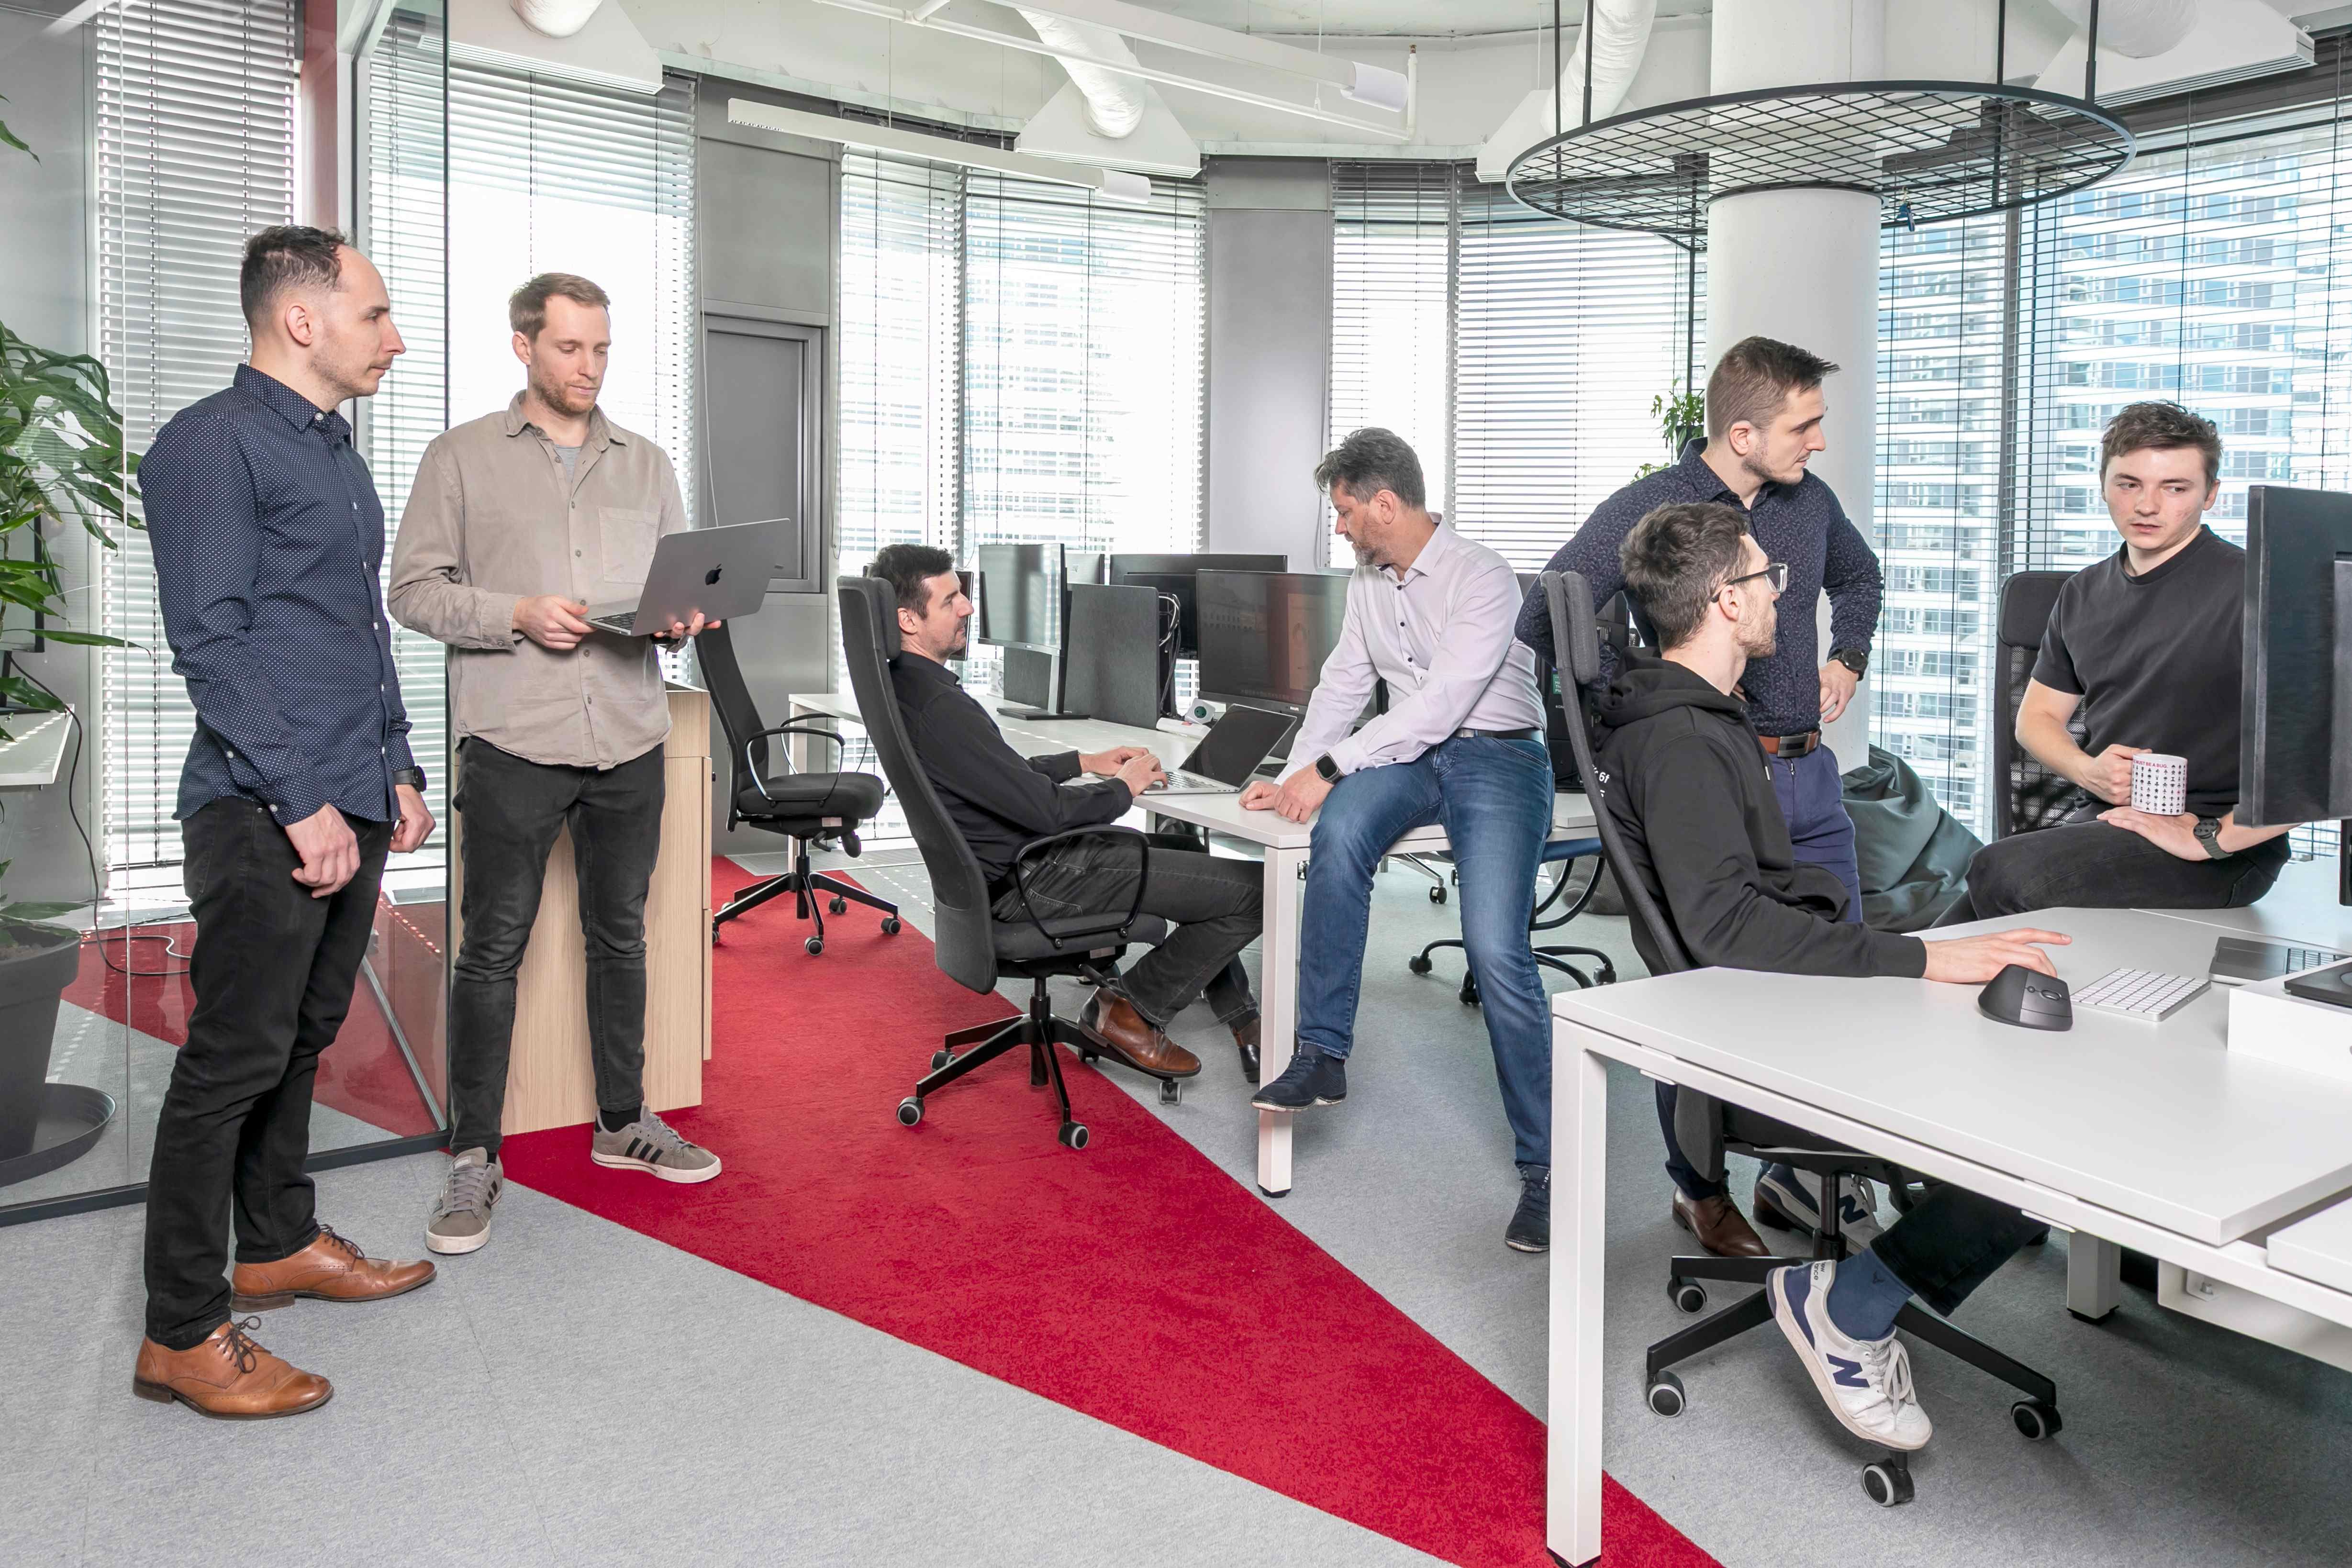
Every social engineering test is conducted by experienced ethical hackers
We use our experience from phishing campaigns, simulated attacks, and Red Teaming operations to create credible scenarios. These scenarios test employee behaviour and internal security processes without putting normal operations at risk.
Book a free consultation
Why choose Citadelo?
Download the free report
We tailor social engineering tests to your industry, environment, and current security maturity. Our experienced ethical hackers draw on real-world campaigns and Red Teaming operations, so they know exactly what an attack looks like in practice.
In 2025, we conducted four times as many social engineering projects as in the previous year. As many as 57% of them contained a critical vulnerability. These results demonstrate that even a technically well-protected organisation may not be prepared for an attack targeting the human factor.
We always emphasise an ethical approach, employee safety, and clear communication of results. We prepare our deliverables so that they can be understood not only by your IT team, but also by HR, legal departments, and company management.
Are you interested in improving your company’s security?
Are you interested in improving your company’s security?
Book now

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2024 citadelo AG. All rights reserved.


Social Engineering vs. Red Teaming
Social Engineering and Red Teaming complement each other. Both services use realistic attack scenarios and help organisations identify weaknesses before real attackers can exploit them. However, they differ in their objectives, scope, and testing methods.
Social engineering testing focuses primarily on the human factor. Using phishing, vishing, smishing, pretexting, and other manipulation techniques, it assesses whether employees can recognise an attack, report it correctly, and follow internal security procedures. The test may target the entire organisation or selected teams and job roles.
Red Teaming goes one step further. It simulates the actions of a real attacker and assesses the resilience of the organisation as a whole. It may combine social engineering with digital attacks, physical intrusion, information gathering, and security team response testing. The objective is to determine whether the organisation can detect, stop, and minimise the impact of a complex attack in time.
When should you choose social engineering testing?
If you want to assess employee security awareness, their responses to phishing attacks, and the effectiveness of incident-reporting processes, a social engineering test is the appropriate choice. If you need to test technologies, people, processes, and physical security within a single comprehensive scenario, choose Red Teaming.