
News
17 September 2026
Security Audit vs. Penetration Test: What Is the Difference and When Do You Need Both?
An audit confirms that your security, procedures and responsibilities are properly defined. But is that enough? Real resilience cannot be assessed on paper alone. Only a penetration test can verify it in practice.
3 September 2026
OWASP Top 10 for LLM 2026: What Actually Changed
In early August, OWASP released the new OWASP Top 10 for LLM Applications. The document roughly tripled in size and now takes real incident data into consideration.
26 August 2026
A document can control your AI without you noticing
We upload contracts, internal analyses and confidential attachments to AI assistants. But what if a document contains not only data, but also a hidden instruction that the AI follows?
25 August 2026
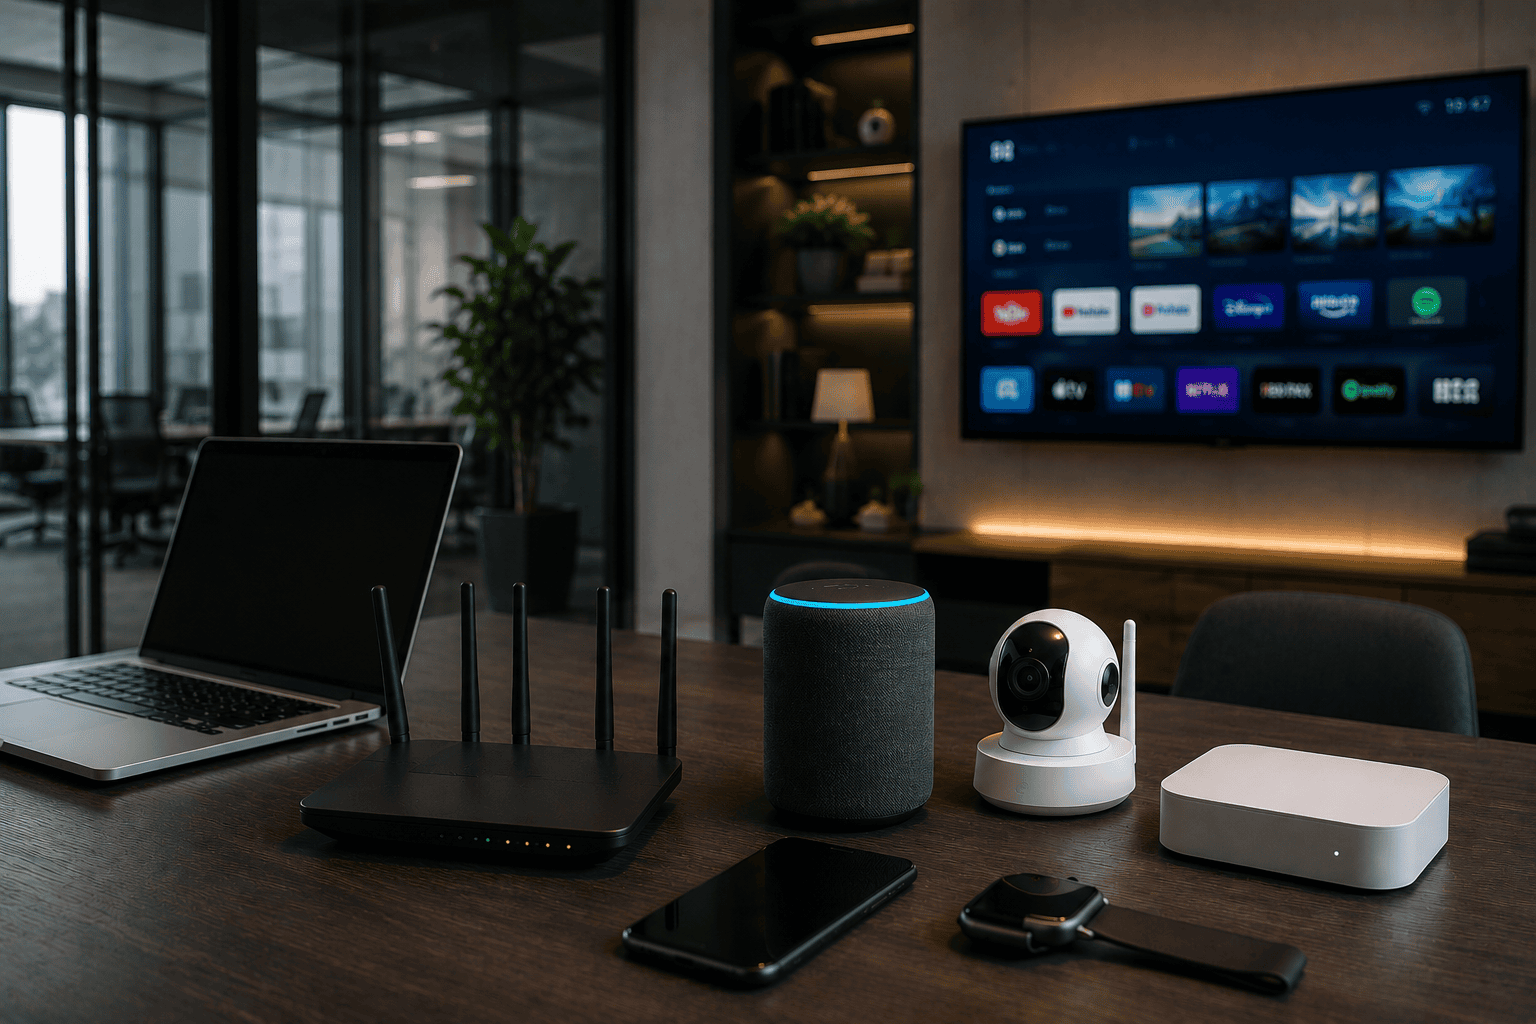
Why We Don’t Think of a TV as a Computer and What the CRA Will Do About It – An Ethical Hacker’s Perspective
What do we think about the CRA after years of taking connected devices apart? Did the CRA arrive at the right time? Will it change anything for ordinary users? And where will it face the greatest practical challenges?
17 August 2026
Cyber Resilience Act: the first deadline is not December 2027. It is 11 September 2026
For an actively exploited vulnerability, you have 24 hours to file the first report.
14 August 2026
The Cyber Resilience Act (CRA): who it applies to, what manufacturers must do, and by when
Product security used to be a commercial decision. The Cyber Resilience Act turns it into a condition for market access in the EU. Here is who the regulation covers, what it requires, which deadlines apply, and where to start.